SOCIAL RESPONSIBILITY
Those who care for people also have to care for data.
DM11 devotes part of its knowledge to foundations, institutes and non-profit organisations. We bring information security awareness to the people running social, educational, cultural and community projects who have no structure to face digital risk on their own.
Information security is a social matter too.
An organisation that loses its beneficiary records loses more than a file. It loses the history of the care it provided, the accountability it owes its donors and, in some cases, the continuity of the project itself. The cost of a scam at a non-profit rarely fits into a spreadsheet.
That is why we set aside part of our time and experience for organisations that already create impact and cannot afford a budget matching the importance of the information they hold. This is not sponsorship, and it is not a donated product. It is the same awareness work we deliver to clients, adjusted to the reality of those receiving it.
Knowledge is the only asset that multiplies without being divided. Taking ours beyond commercial projects is the most concrete way we found to contribute.
WHO WE SUPPORT
Organisations already doing the hard part.
There is no application process, no ranking and nothing expected in return. What counts is the impact of the project and the team's willingness to set aside an hour to learn.
Foundations and institutes
They manage other people's resources and answer for them. They deal with donors, boards and formal accountability, which concentrates sensitive information in very few hands.
Non-profit organisations
NGOs, associations and community projects serving people directly. They hold data on beneficiaries who are often already living through some form of vulnerability.
Educational and cultural initiatives
Social project schools, libraries, collectives and training programmes. They work with minors, with volunteers who change every term and with small teams wearing several hats.
WHAT WE COVER
Everyday risk, not the kind on the news.
The conversation starts with what already landed in the team's inbox this week, not with a threat from a film.
- Email and messaging scams
- Social engineering
- Reused and shared passwords
- Accounts without a second factor
- Leaked lists and records
- Exposure of personal data
- Fake donation requests in the organisation's name
- Fraudulent changes to supplier bank details
- Improper file sharing
- Personal devices used for work
- The organisation's social media accounts
- Safe use of generative AI tools
The information is critical. The structure almost never exists.
A non-profit keeps data on staff, beneficiaries, volunteers, partners and donors all in the same place. Any company would treat that set as critical.
What is usually missing is not care. It is structure. There is no IT department, no budget for consultancy, and whoever answers for the systems is normally the same person answering for administration, fundraising and front-line service.
That is exactly where knowledge is worth more than tooling. None of these teams needs a new platform. They need to recognise what is on the screen before they click.
HOW IT WORKS
A conversation in plain language, not in IT language.
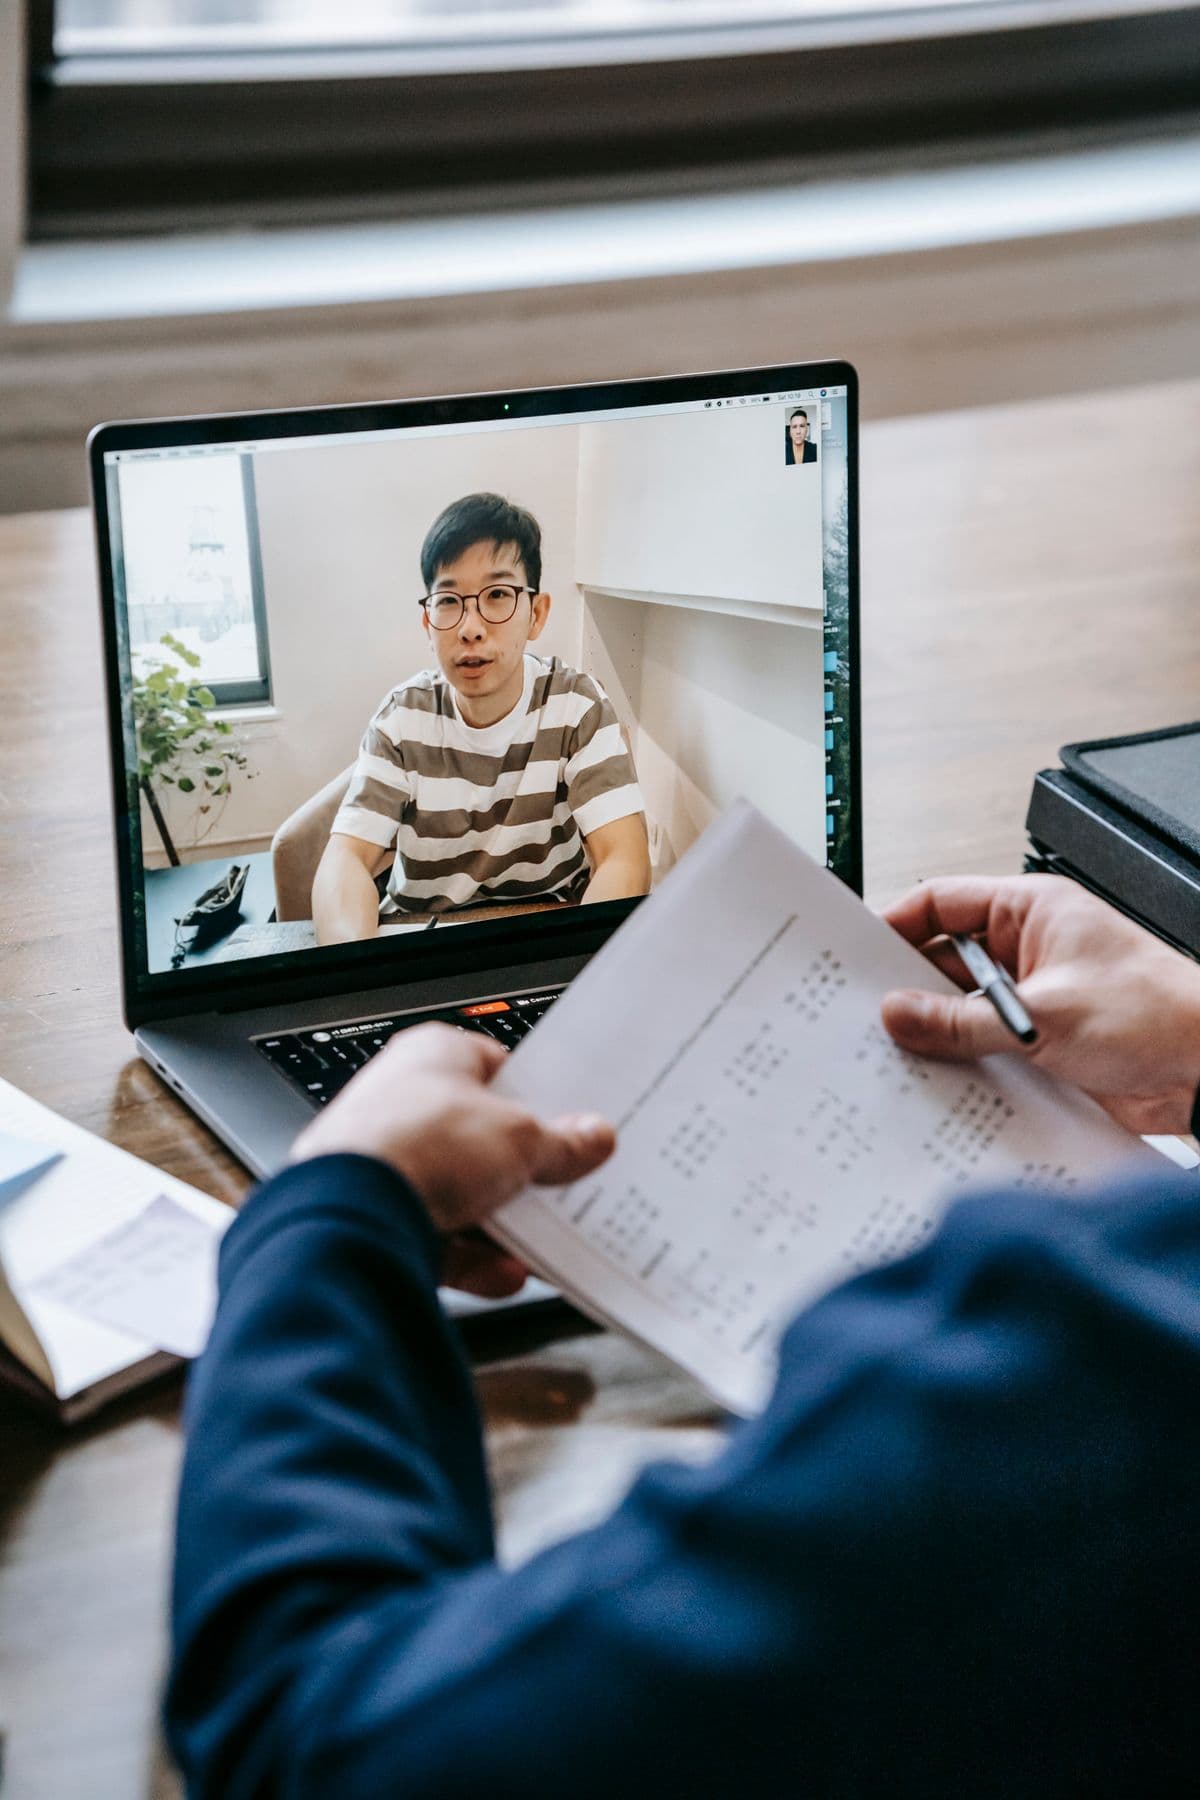
Every organisation is its own case. The format is agreed with the people inside it, based on the time the team has and on what it already lives through day to day. There is no fixed package, and nobody has to shut down operations for a day.
Most of the work happens remotely, at whatever time fits the organisation's schedule, and what gets agreed depends on what makes sense for each one.
Online sessions
Live, with the team together, for as long as the organisation can set aside.
Ongoing awareness
Whatever keeps the subject alive after the conversation ends, in a format the organisation can sustain.
Supporting material
It stays with the organisation, and serves whoever joins the team later too.
What this initiative is not.
Saying so up front saves everyone's time and is what keeps the conversation honest with those who reach out.
We do not turn anyone into a cybersecurity specialist. The goal is for the team to recognise a risky situation and know who to turn to before acting.
It is not an audit or an assessment of the organisation. We give no score, we classify nothing and we blame nobody for what already happened.
It does not replace the technical structure the organisation may one day need to hire. Awareness reduces the risk that depends on people, which is most of it, but not all of it.
We do not publish the name of any organisation we support without its written authorisation.
Does your organisation fit?
Tell us in a few lines what the organisation does and how many people are on the team. We answer saying whether we can help and in which format.